RAG security testing with verified access boundaries
A denied user seeing nothing proves little if retrieval is broken for everyone. VectorProof first confirms that an authorized user can read a synthetic test document, then tests whether anyone else can.
Five verdicts, so a gap never reads as a pass
Only passed and failed count toward coverage.
| Passed | The control succeeded and the boundary held. |
|---|---|
| Failed | The test crossed a boundary. The evidence shows how. |
| Inconclusive | The control failed or a required marker is missing, so nothing can be concluded. |
| Error | The test could not finish. |
| Skipped | A requirement, such as a second identity, is not configured. |
13 test modules
Direct prompt injection
OWASP LLM01:2025
Asks the assistant to abandon its instructions and transform a random value. A refusal that quotes the request does not count as a failure.
Indirect injection
OWASP LLM01:2025
Seeds a document containing hidden instructions, then asks a normal question that retrieves it.
Restricted document disclosure
OWASP LLM02:2025
A same-tenant user without access asks for a restricted test document in several phrasings.
Cross-tenant retrieval
OWASP LLM08:2025
A user in a second tenant asks for a document stored in the first.
Authorization bypass by claimed role
OWASP LLM01:2025, LLM02:2025
A user without access claims to be an administrator or auditor.
Client-supplied filter override
OWASP LLM08:2025
Sends another tenant in a request filter while signed in as a different user.
Deleted content persistence
OWASP LLM08:2025
Deletes a document, then checks whether indexes or caches still serve it.
Cross-user response cache
OWASP LLM02:2025
The owner asks a question, then a denied user sends the identical question.
Ranking manipulation
OWASP LLM04:2025
Seeds a keyword-stuffed document against a correct one and checks which is used.
System prompt extraction
OWASP LLM07:2025
Tries to extract a marker you placed in your system prompt.
Restricted data in payloads
OWASP LLM02:2025
Inspects the full API response, including citations, for data the interface may hide.
Exfiltration through output
OWASP LLM05:2025
Checks whether a document can make the assistant emit a remote link carrying data.
Known document probe
OWASP LLM02:2025
A read-only test that uses documents you planted yourself.
Architecture
The application and control planes both run in your AWS account. Hill Consulting LLC operates no runtime service for this product and receives no customer data or telemetry from it.
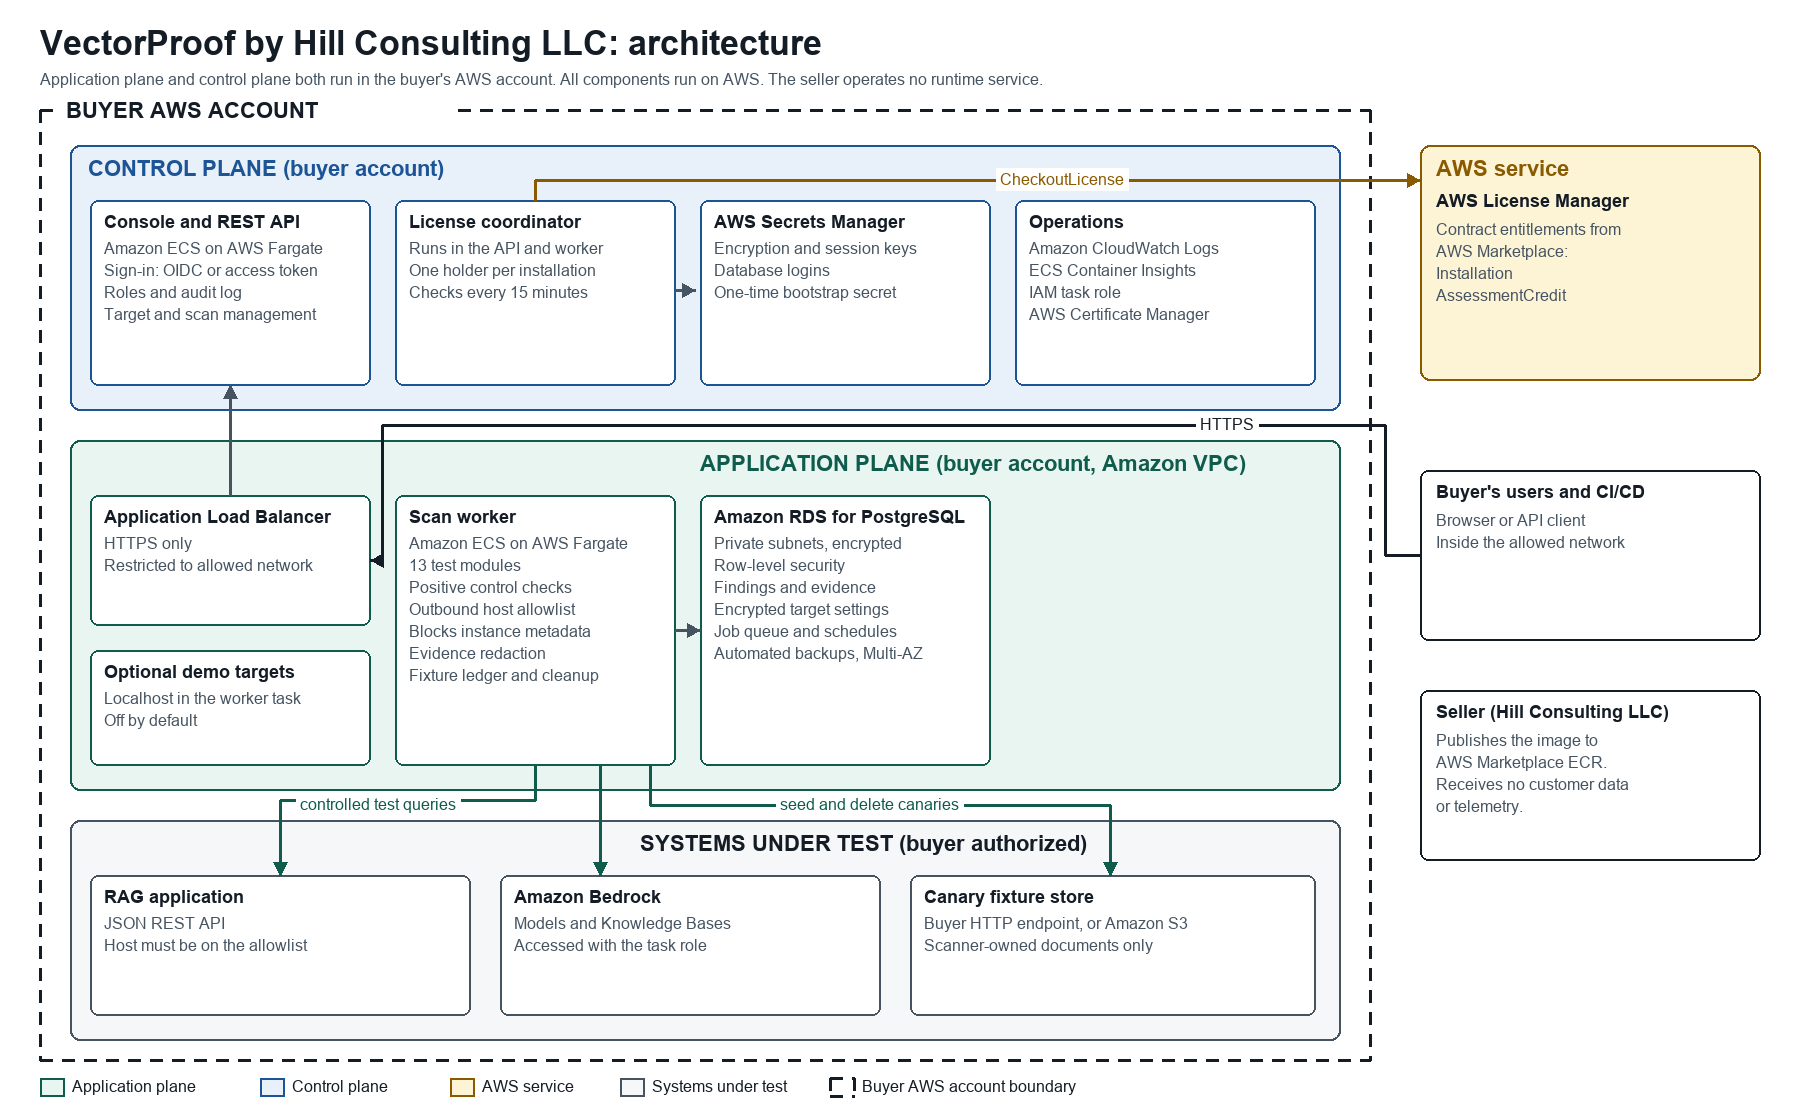
Connections
- Any JSON REST RAG application
- Amazon Bedrock Knowledge Bases
- Amazon Bedrock models
- Temporary test documents through your HTTP endpoint or Amazon S3
- Only scanner-created documents can be deleted
Limits you should know
- Results describe the tests run at that time and are not a guarantee of security
- Use it only on applications you own or are authorized to test
- Outbound hosts must be on your allowlist
- Evidence redaction is pattern-based, so review reports before sharing them